---
updatedAt: 2025-10-02T13:18:36.000Z
agentTools:
  projectIndex: https://developer.alloy.com/public/llms.txt
---

# JumpCloud

## 1. Access to Authentication Settings at Alloy

### 1.1 Granting Access to the SAML Self-Serve Setup

The agent must either have `Admin` access or be granted access to a role with the following permissions below via “Roles” to “Authentication Settings.”

<Image align="center" src="https://files.readme.io/9f966b0f80f171014cc86dc7bdf7bf2ebd2051d75d94135318f52762c76c23e8-Screenshot_2025-01-03_at_10.21.12_AM.png" />

### 1.2 Configuring a Default Role

Before you can use SAML, you **MUST** configure a default role for your users in the Alloy settings. This role will determine the permissions that your user has when they first log in.

The first time a user logs in using SAML SSO, they will be added to the Alloy system as an "Agent" and will be given this default role. Agents with Admin permission can then go in and assign them a different role, if they need additional privileges.

1. Be sure that you have Admin permission in Alloy and log in to your dashboard.

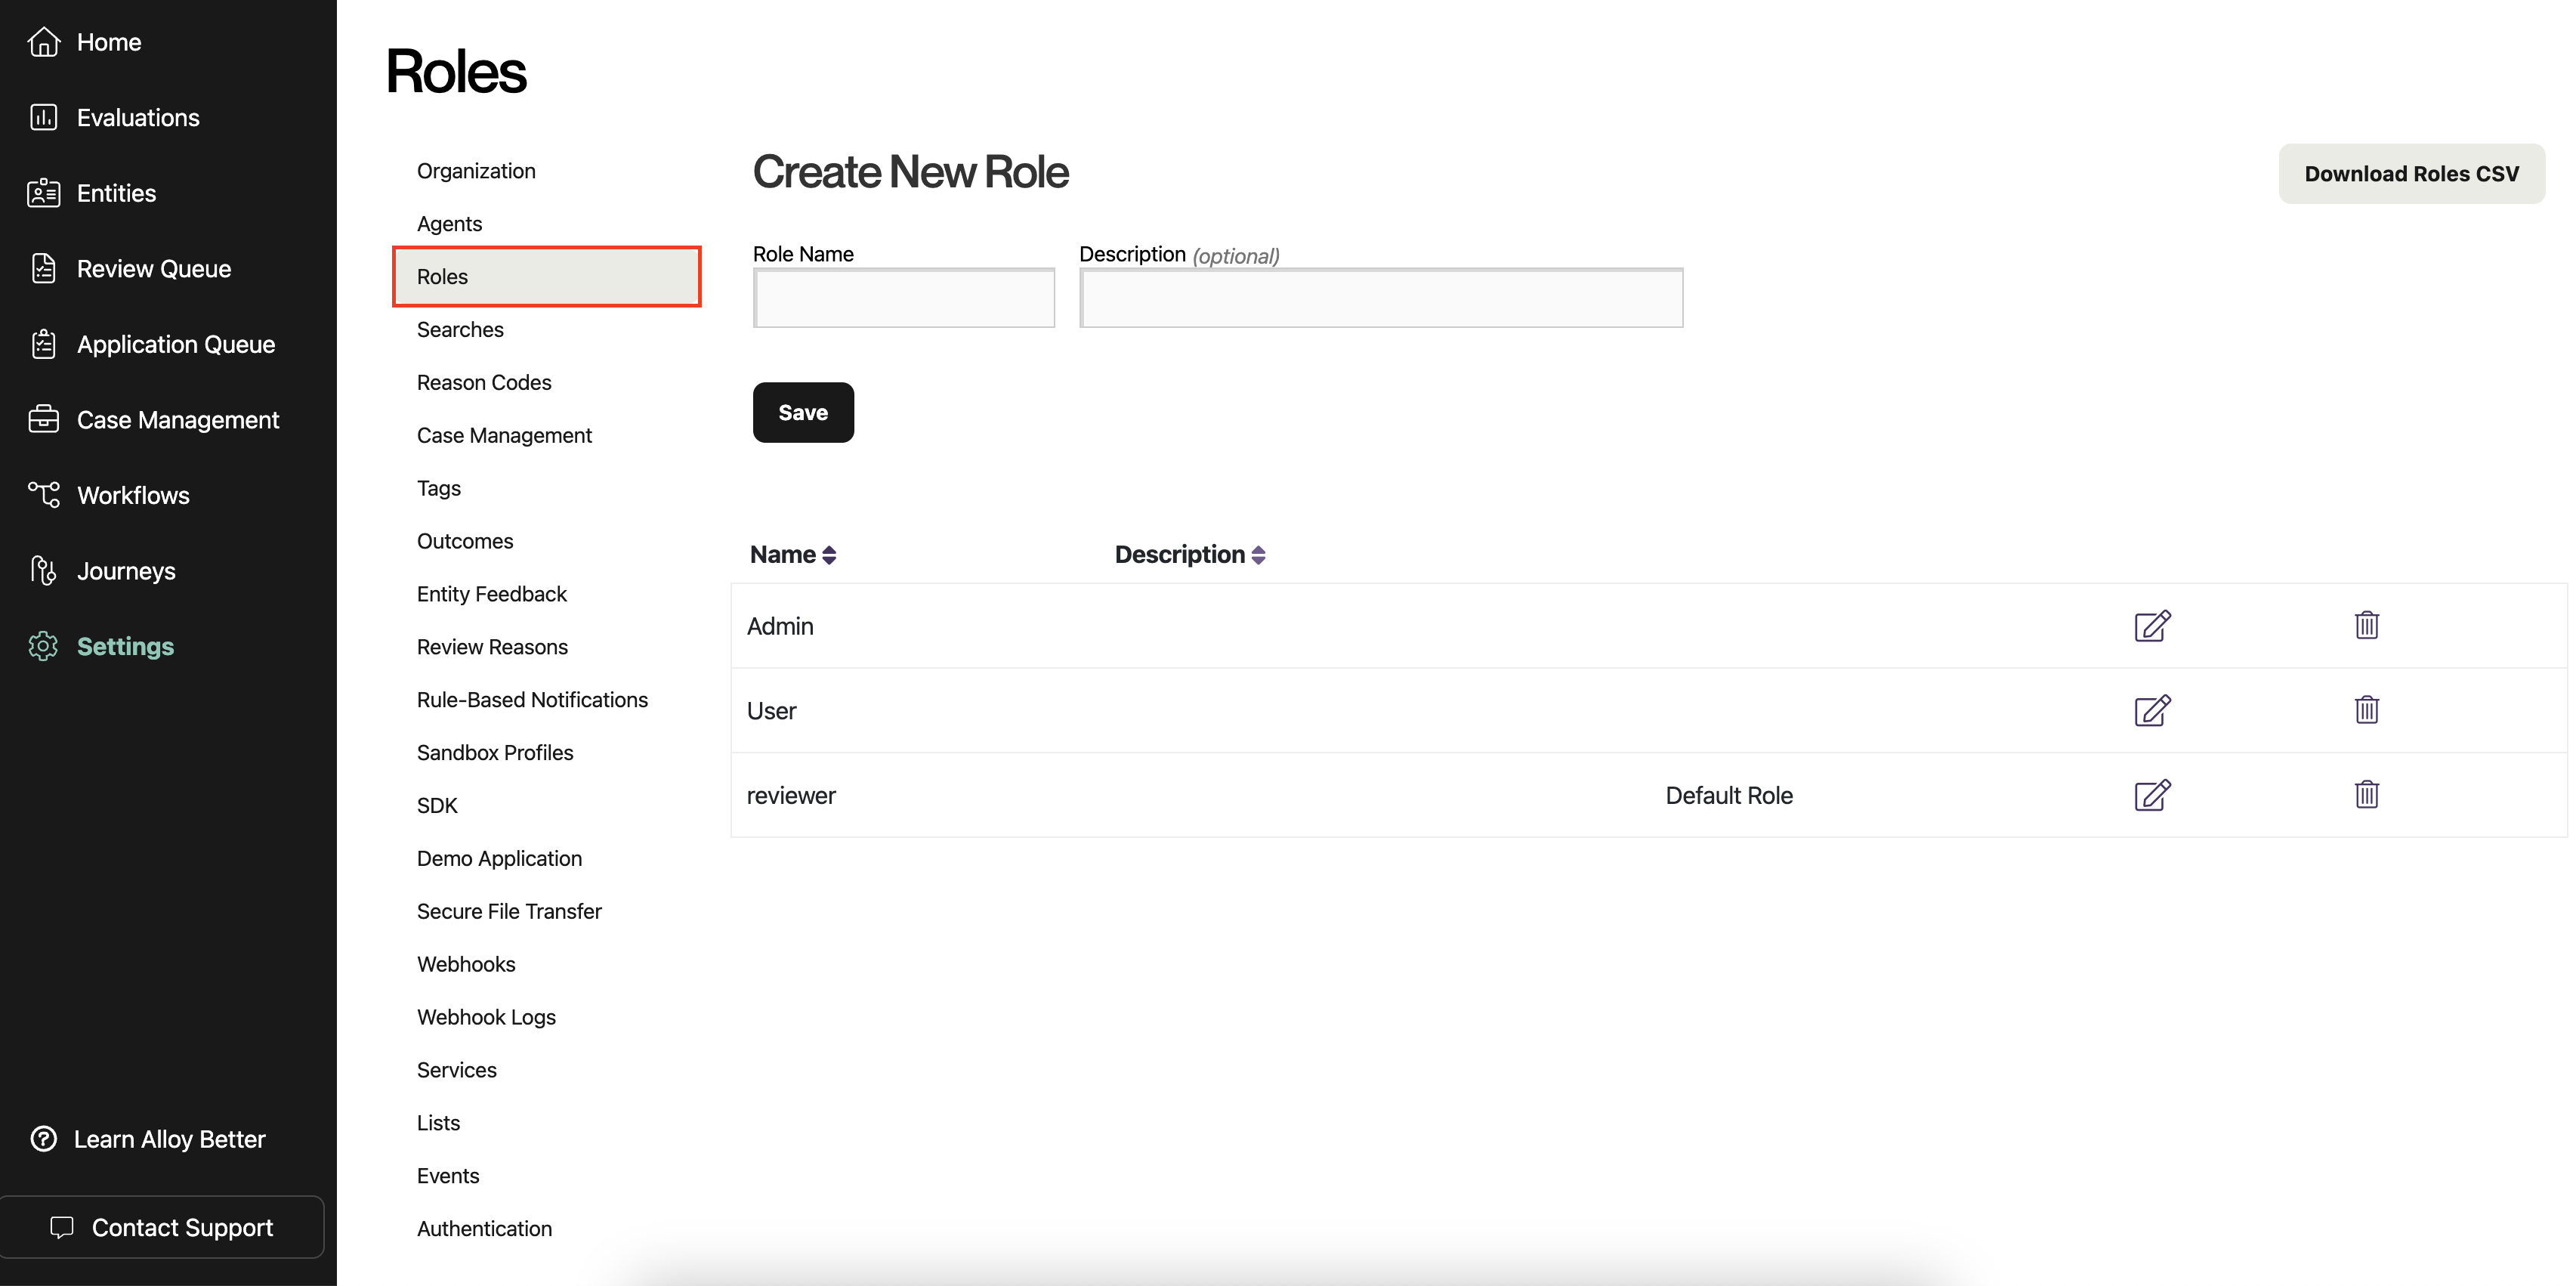
2. Navigate to **Settings** in the sidebar, and then select **Roles** from the list.

   <Image title="Screen Shot 2021-11-08 at 2.26.15 PM.png" alt="An image showing the Alloy Roles page." align="center" src="https://files.readme.io/18437d4-a1.png" />

3. On the Roles page, you should see a list of roles. By default, these include "Admin" and "User," but your organization may have configured different ones.
   ![](https://files.readme.io/cd0a3d424793cd5d685e05936e8cd0d16d07f97d3081764368e80d39b3307bd2-image.png)

4. Select the role that you want to designate as the default for new SAML users. Click the icon with a pencil to edit the role. (You could also create a new role first by filling out the form at the top and clicking "Save.")

   <Image alt="You do not want to select the Admin role, unless you want all of your users to have full control over your data and settings in Alloy." align="center" src="https://files.readme.io/e467fe6062ff397b05b6be313bd8fae1ff533dd4631899c6ec1535d52188ff14-image.png">
     You do not want to select the Admin role, unless you want all of your users to have full control over your data and settings in Alloy.
   </Image>

5. Check the box labeled "Designate this role as the organizational default for new users," and apply your changes by clicking "Save."

   <Image title="Screen Shot 2021-11-08 at 2.33.09 PM.png" alt="A screenshot showing the default role setting." align="center" src="https://files.readme.io/362afac-a4.png" />

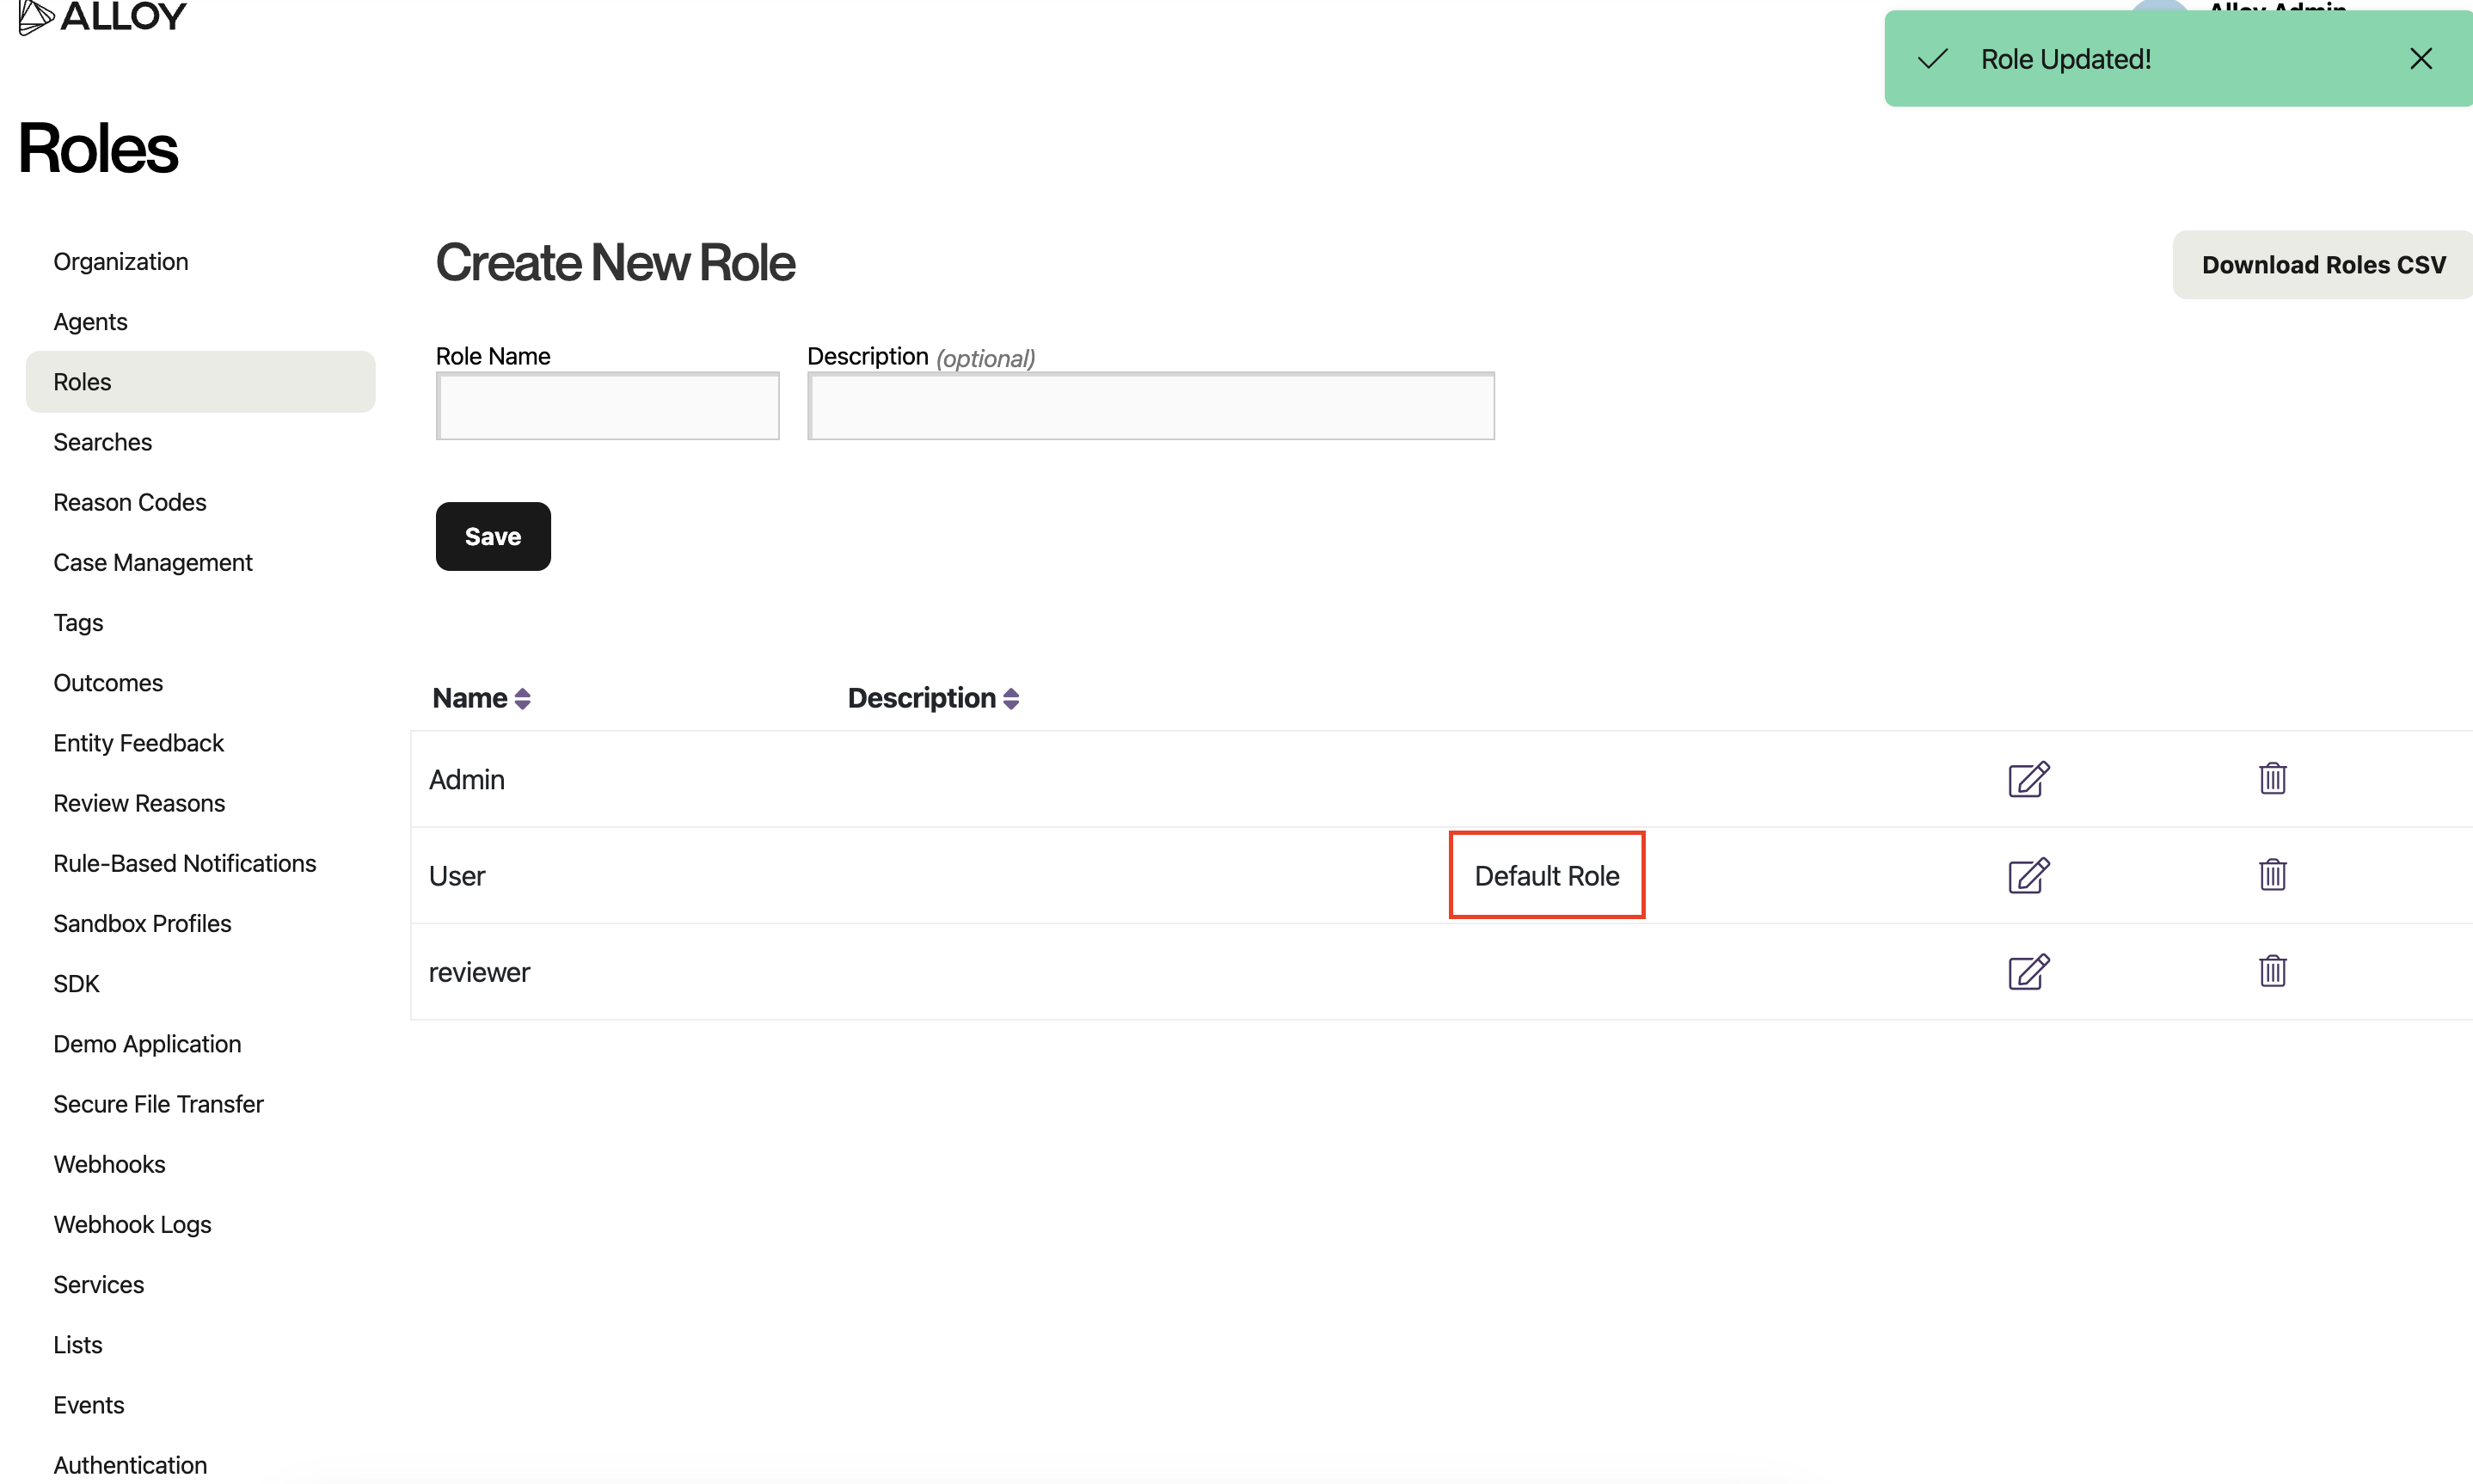
6. You have now set a default user role for your organization and are ready to use SAML! Notice the addition of the "Default Role" label that will tell you your default role when you return to this page in the future.
   ![](https://files.readme.io/4156b80d1bdafcf9739f042f108ea0d4c640d0bfa2169f732f6489f9cacb4c78-image.png)

### 1.3 Setting up SAML

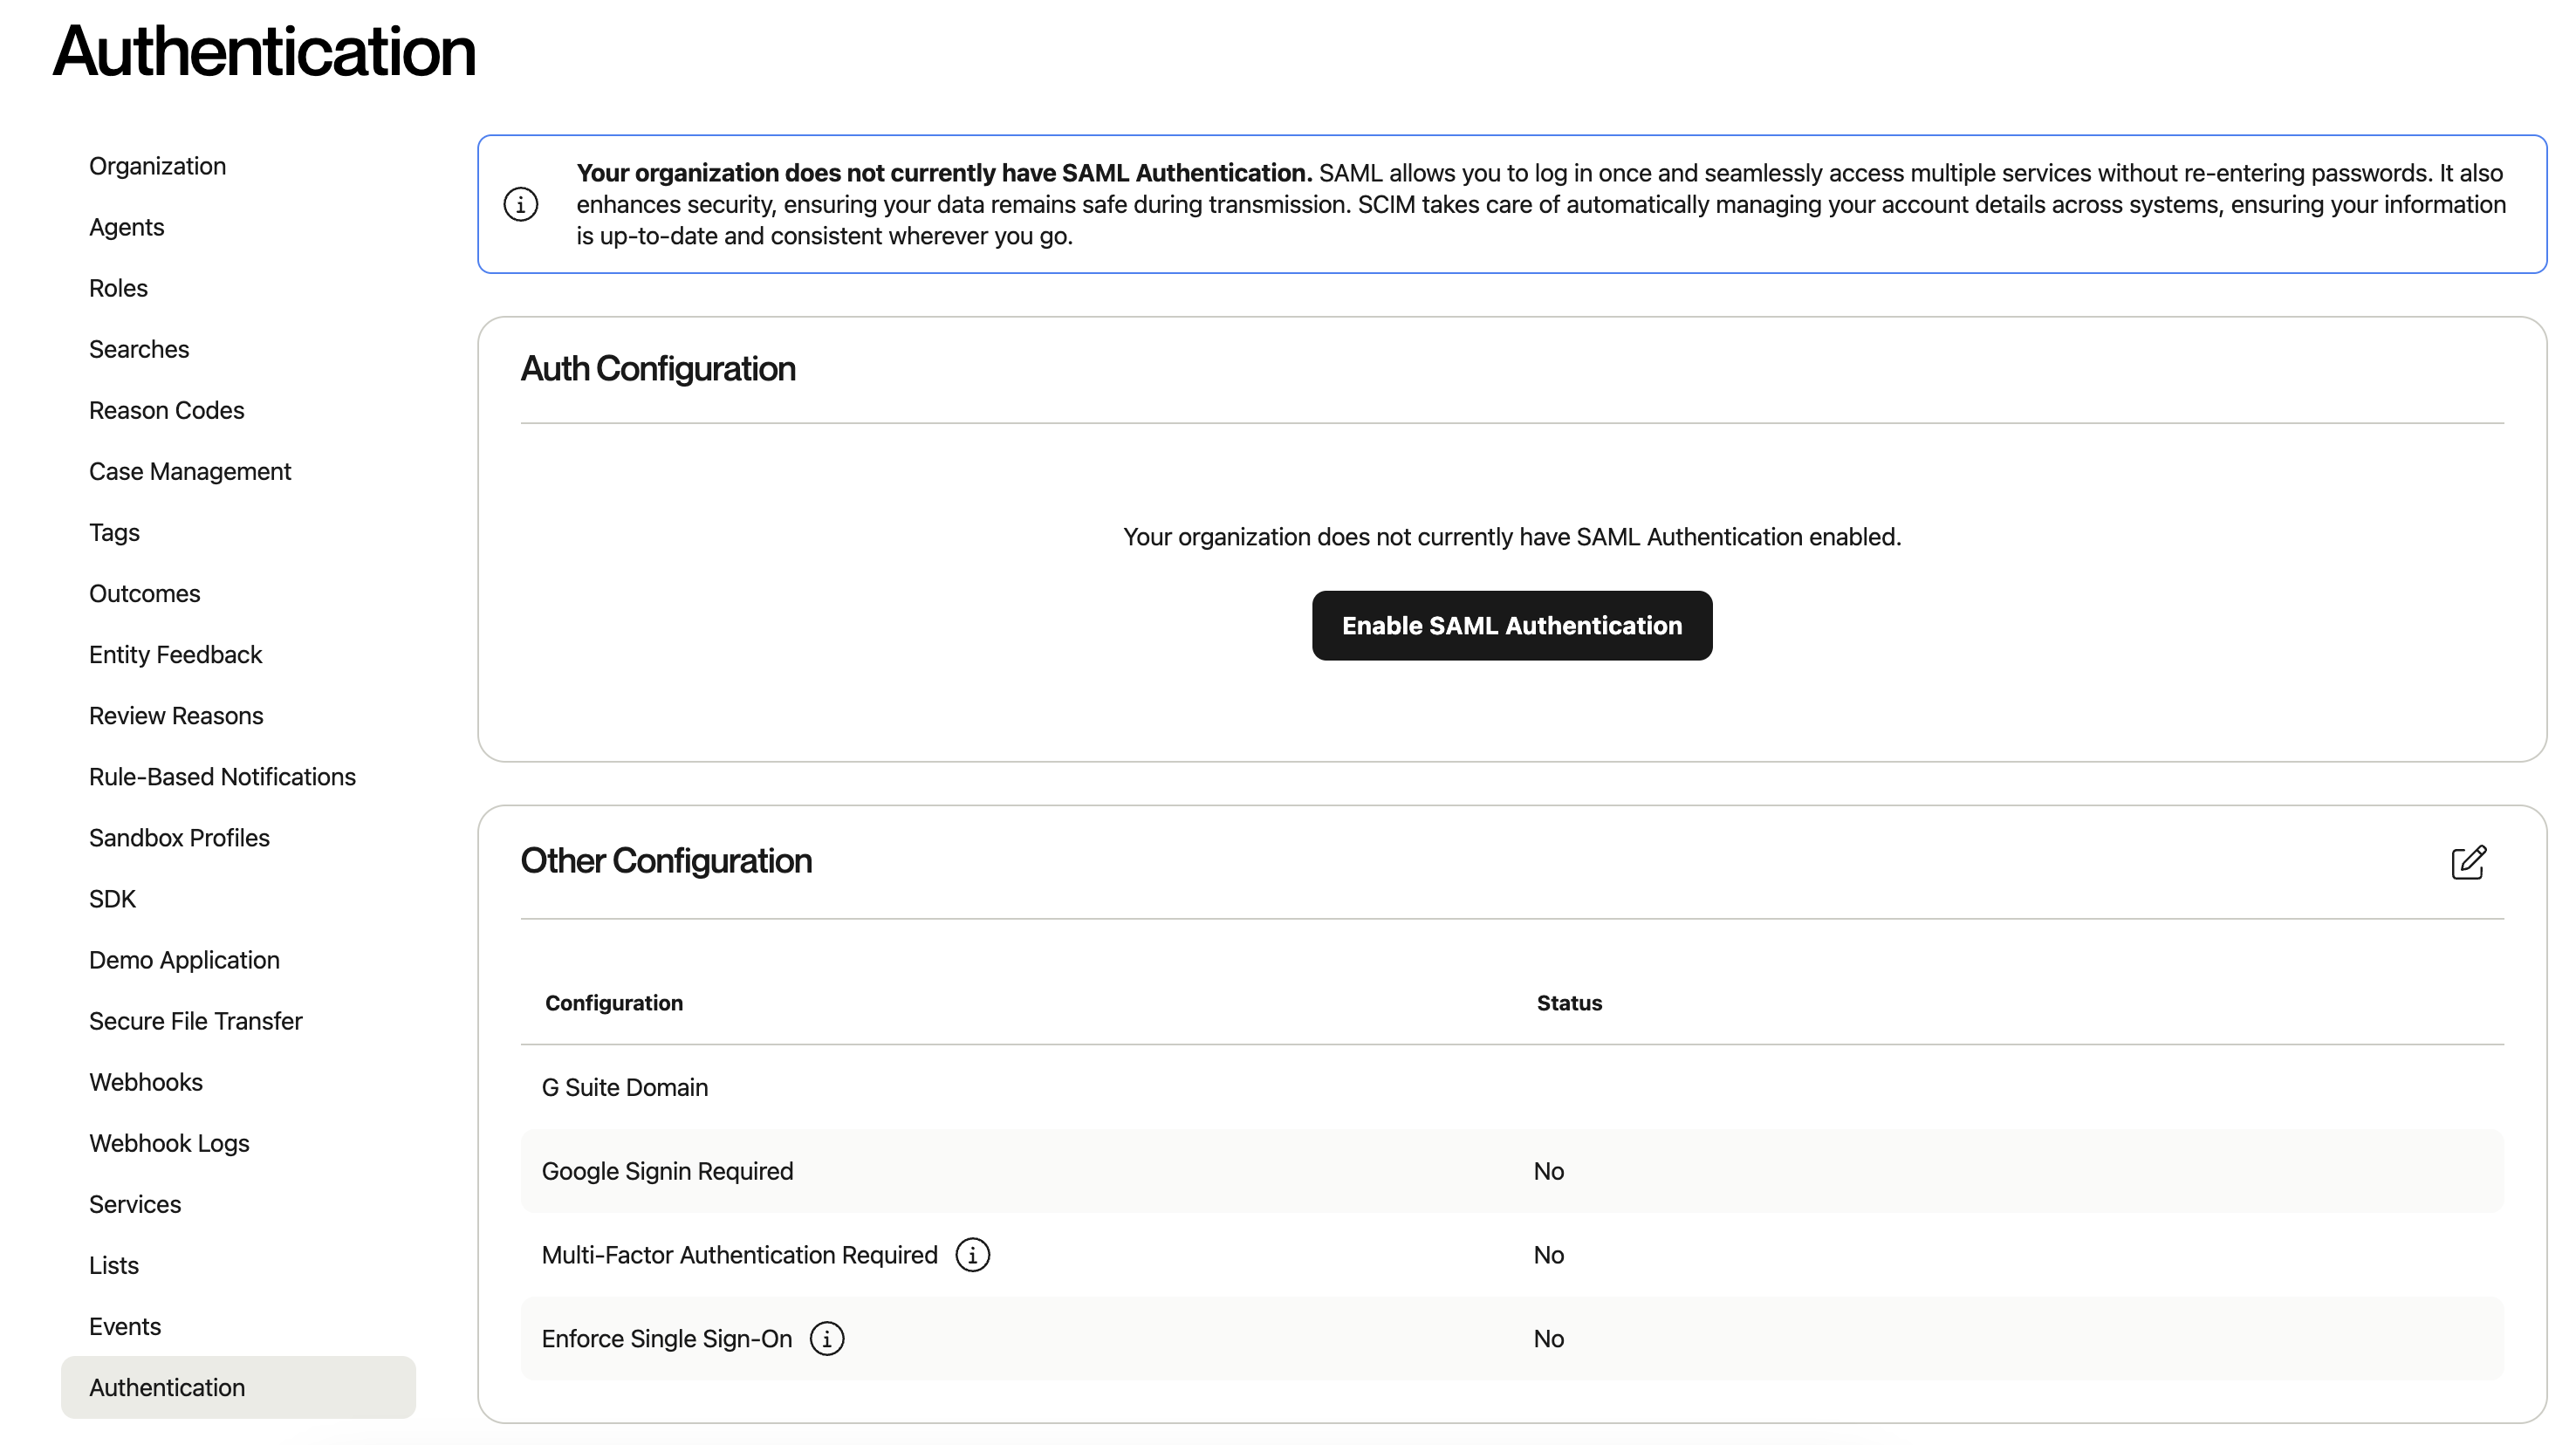
Once your access has been configured, go to “Authentication.”
![](https://files.readme.io/32957ef8d11ddfa4f162d4f3f6dbe3d57c3f354982c705e0cd05894e07bbf899-image.png)

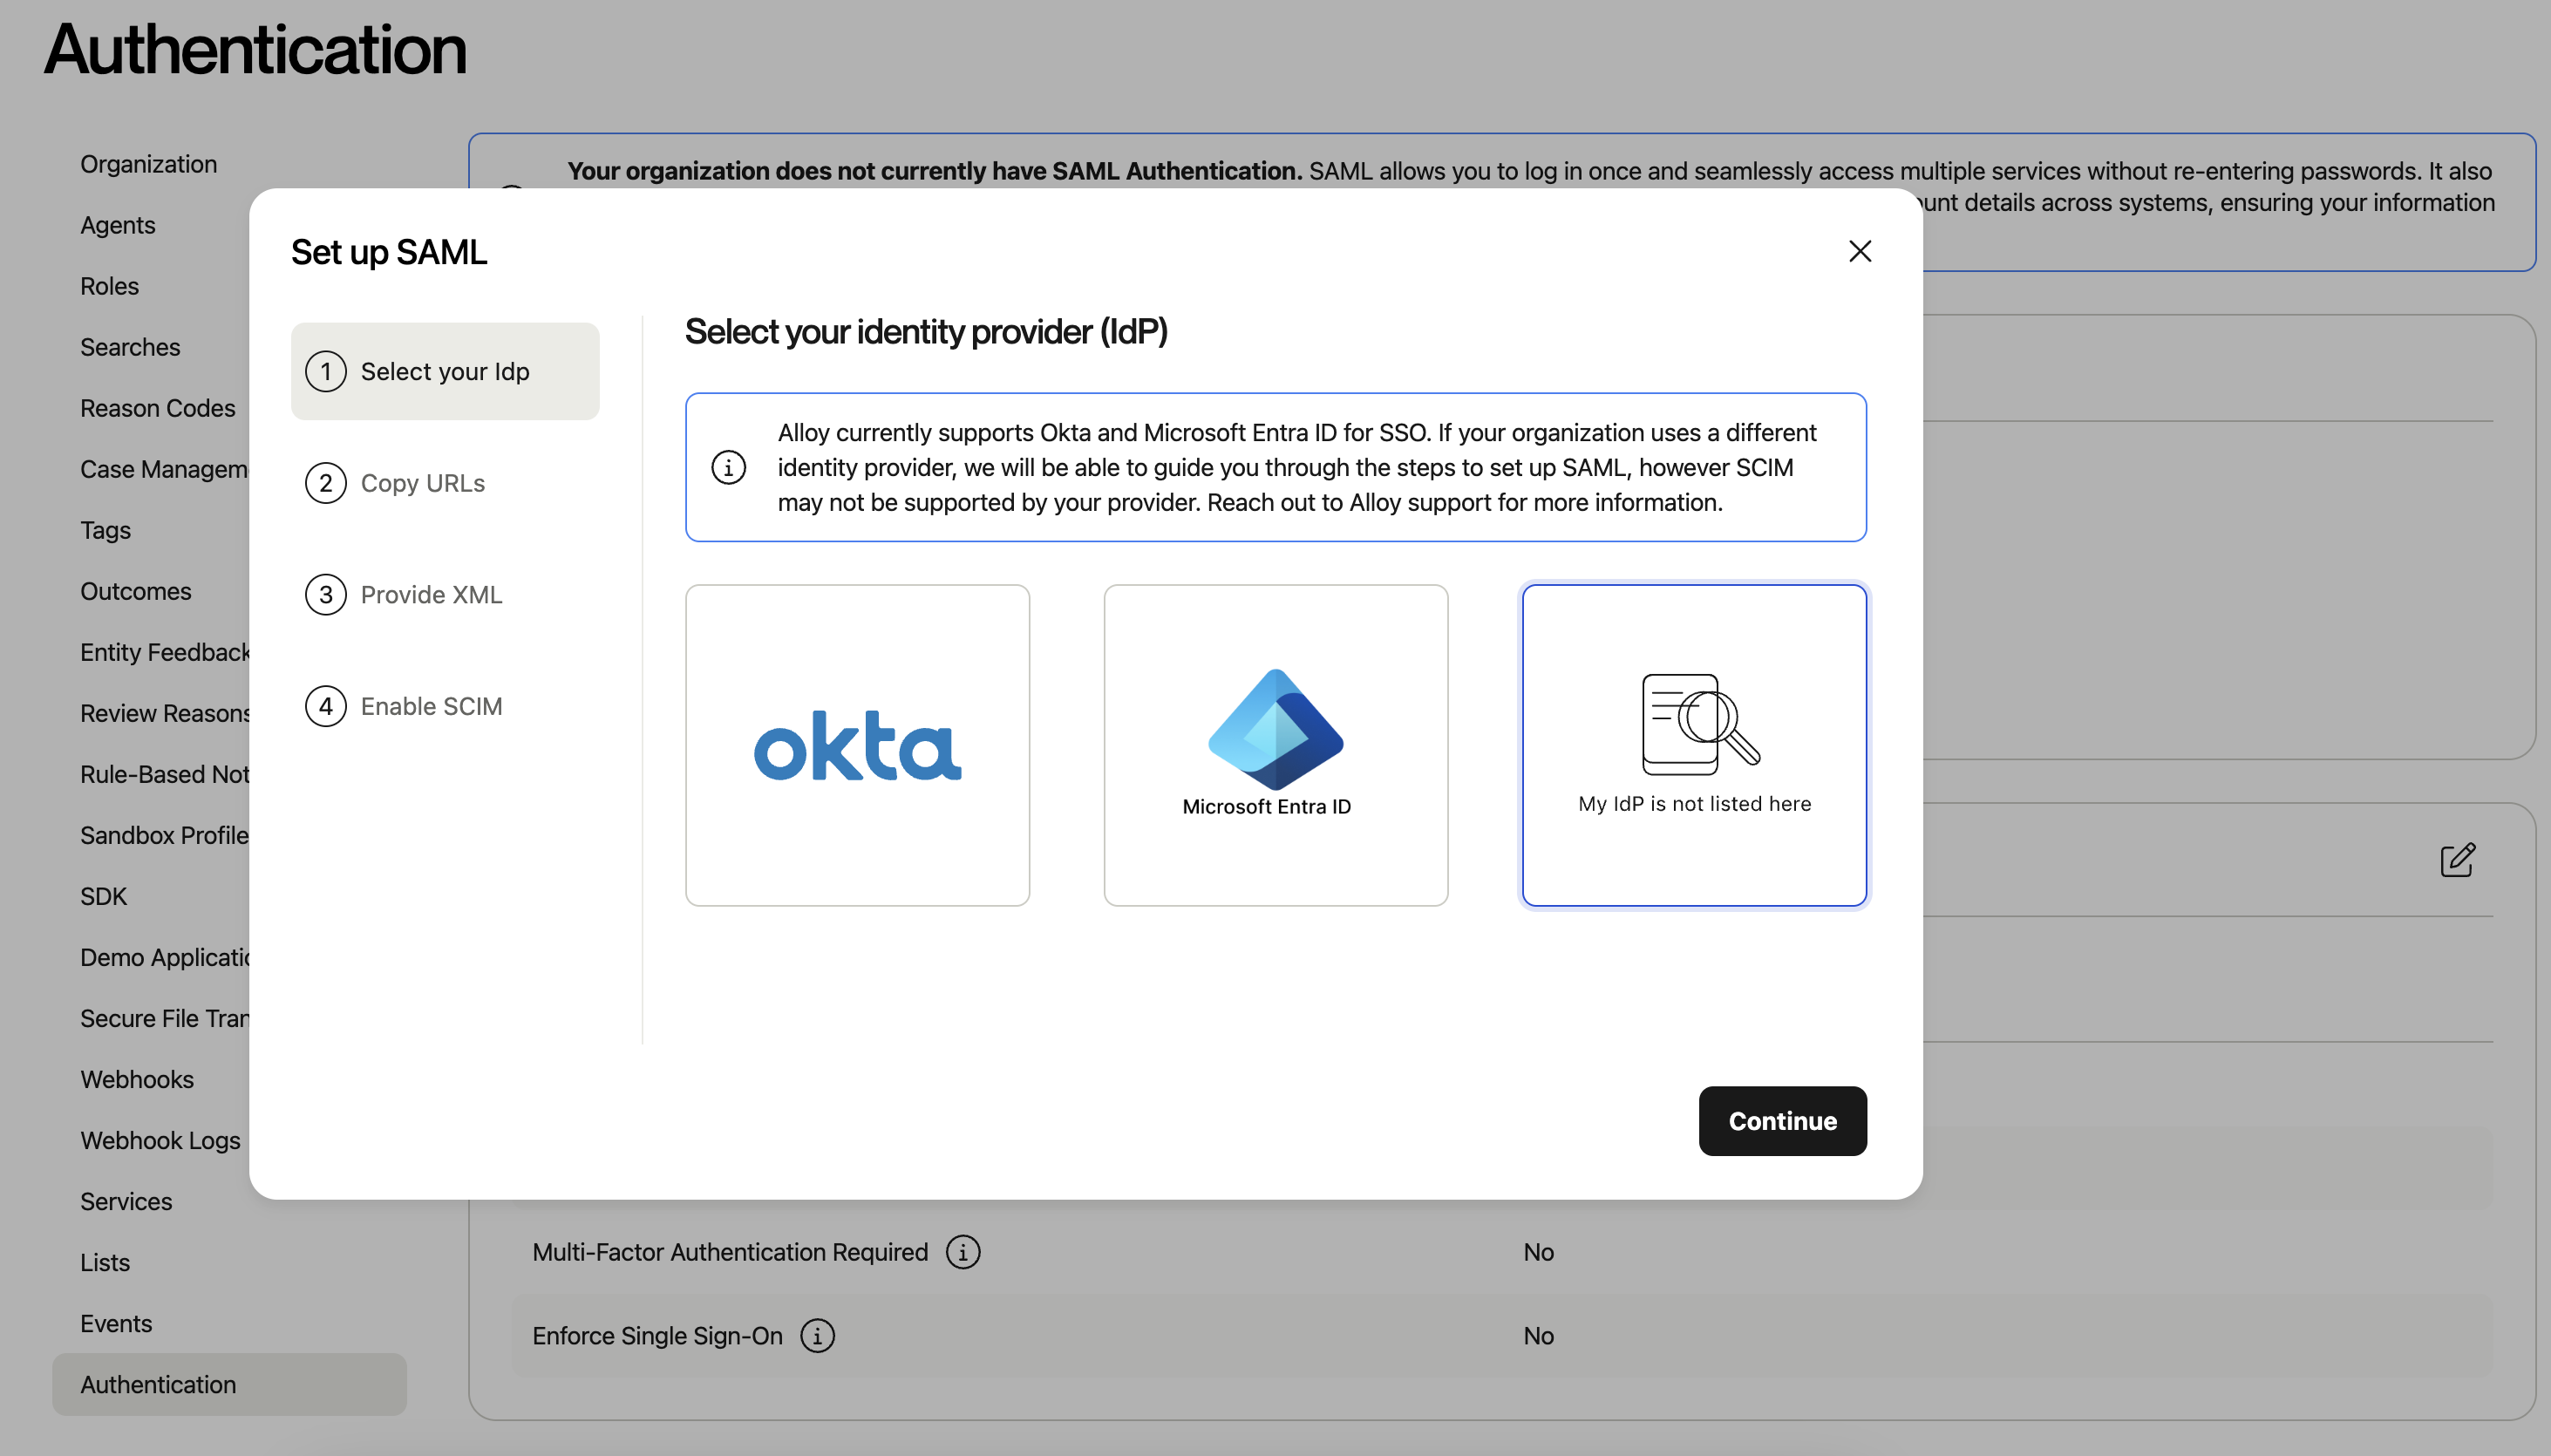
Then, select “Enable SAML Authentication.”
![](https://files.readme.io/0a7b068c2c1b59da53d30d221ea4ea9ffd96f707a857a62ef6bda8d7e7ddfc01-image.png)

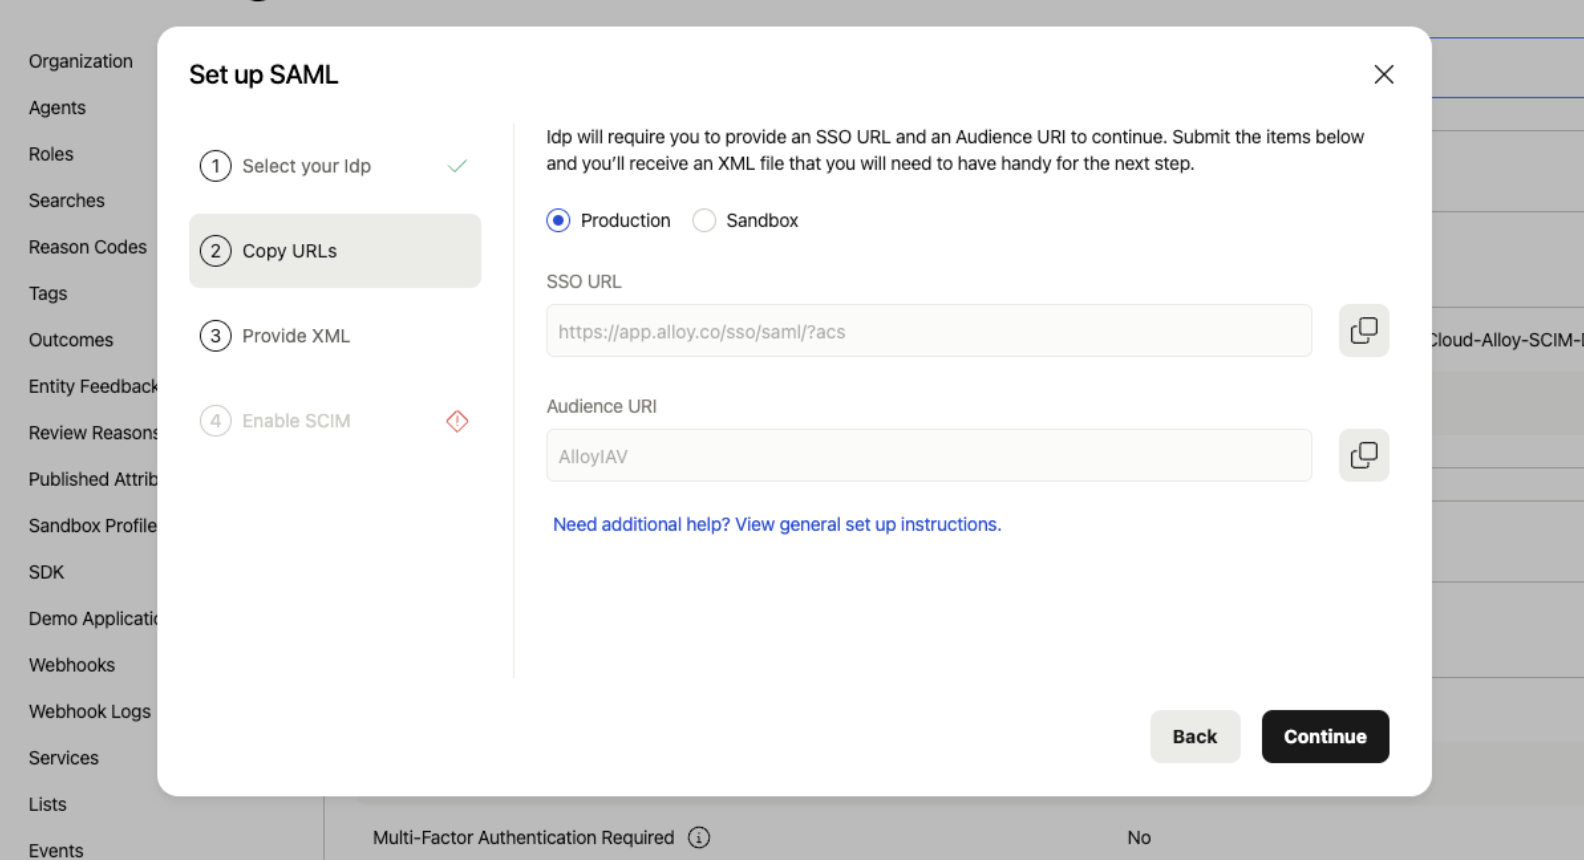
Select `My Idp is not listed here` box and click Continue.
![](https://files.readme.io/f7793aef09950d099c50b435bba57806d578b6505dd6b5eba9381d60e3dae7d2-image.png)

Take note of the `SSO URL` and `Audience URI.`

***

## 2. Add Alloy to JumpCloud

### 2.1 Create an application on JumpCloud

<Image title="Screenshot 2024-04-26 at 6.00.28 PM.png" alt="Creating an application on JumpCloud." align="center" src="https://files.readme.io/a4c8c61-1.png" />

<Image title="Screenshot 2024-04-26 at 6.00.28 PM.png" alt="Adding details for the JumpCloud application." align="center" src="https://files.readme.io/33eb1b5-2.png" />

<Image title="Screenshot 2024-04-26 at 6.00.28 PM.png" alt="Configuring settings in JumpCloud." align="center" src="https://files.readme.io/921bd3f-3.png" />

<Image title="Screenshot 2024-04-26 at 6.00.56 PM.png" alt="Screenshot showing advanced settings in JumpCloud." align="center" src="https://files.readme.io/6db6020-4.png" />

<Image title="Screenshot 2024-04-26 at 6.01.22 PM.png" alt="Attribute mapping details in JumpCloud." align="center" src="https://files.readme.io/3e0bac8-5.png" />

<Image title="Screenshot 2024-04-26 at 6.01.22 PM.png" alt="Finalizing the application setup in JumpCloud." align="center" src="https://files.readme.io/436ace2-6.png" />

### 2.2 Configure the Application

1. Add the IdP Entity ID:
   * Use a unique Entity ID. The pattern can be `JumpCloud-Alloy-<your-organization-name-slug>`. For example: `JumpCloud-Alloy-demo-bank`.

2. Add the SP Entity ID:
   * This is the `Audience URI` shown in step 1.3.

3. Add ACS URLs:

   * This is the `SSO URL` shown in step 1.3.

   <Image title="Screenshot 2024-04-26 at 6.02.21 PM.png" alt="Configuring ACS URLs in JumpCloud." align="center" src="https://files.readme.io/ddd1c11-7.png" />

4. Check `Declare Redirect Endpoint`:

   <Image title="Screenshot 2024-04-26 at 6.03.10 PM.png" alt="Declaring redirect endpoint in JumpCloud." align="center" src="https://files.readme.io/131db3e-8.png" />

5. Add Attribute mapping:

   * `Email`: User's email address (`email`).
   * `firstName`: User's first name (`firstName`).
   * `lastName`: User's last name (`lastName`).
   * `phone`: User's phone number (`phoneNumbers.work`).

   <Image title="Screenshot 2024-04-26 at 6.04.28 PM.png" alt="Adding attribute mappings in JumpCloud." align="center" src="https://files.readme.io/f12aa6b-9.png" />

6. Save your configuration:

   <Image title="Screenshot 2024-04-26 at 6.04.37 PM.png" alt="Saving JumpCloud application settings." align="center" src="https://files.readme.io/5e210b0-10.png" />

7. Download the `Metadata XML`. You will need to upload this metadata to Alloy.

   <Image title="Screenshot 2024-04-26 at 6.04.57 PM.png" alt="Downloading metadata XML from JumpCloud." align="center" src="https://files.readme.io/3d8c663-11.png" />

***

## 3. Upload the IdP Metadata to Alloy

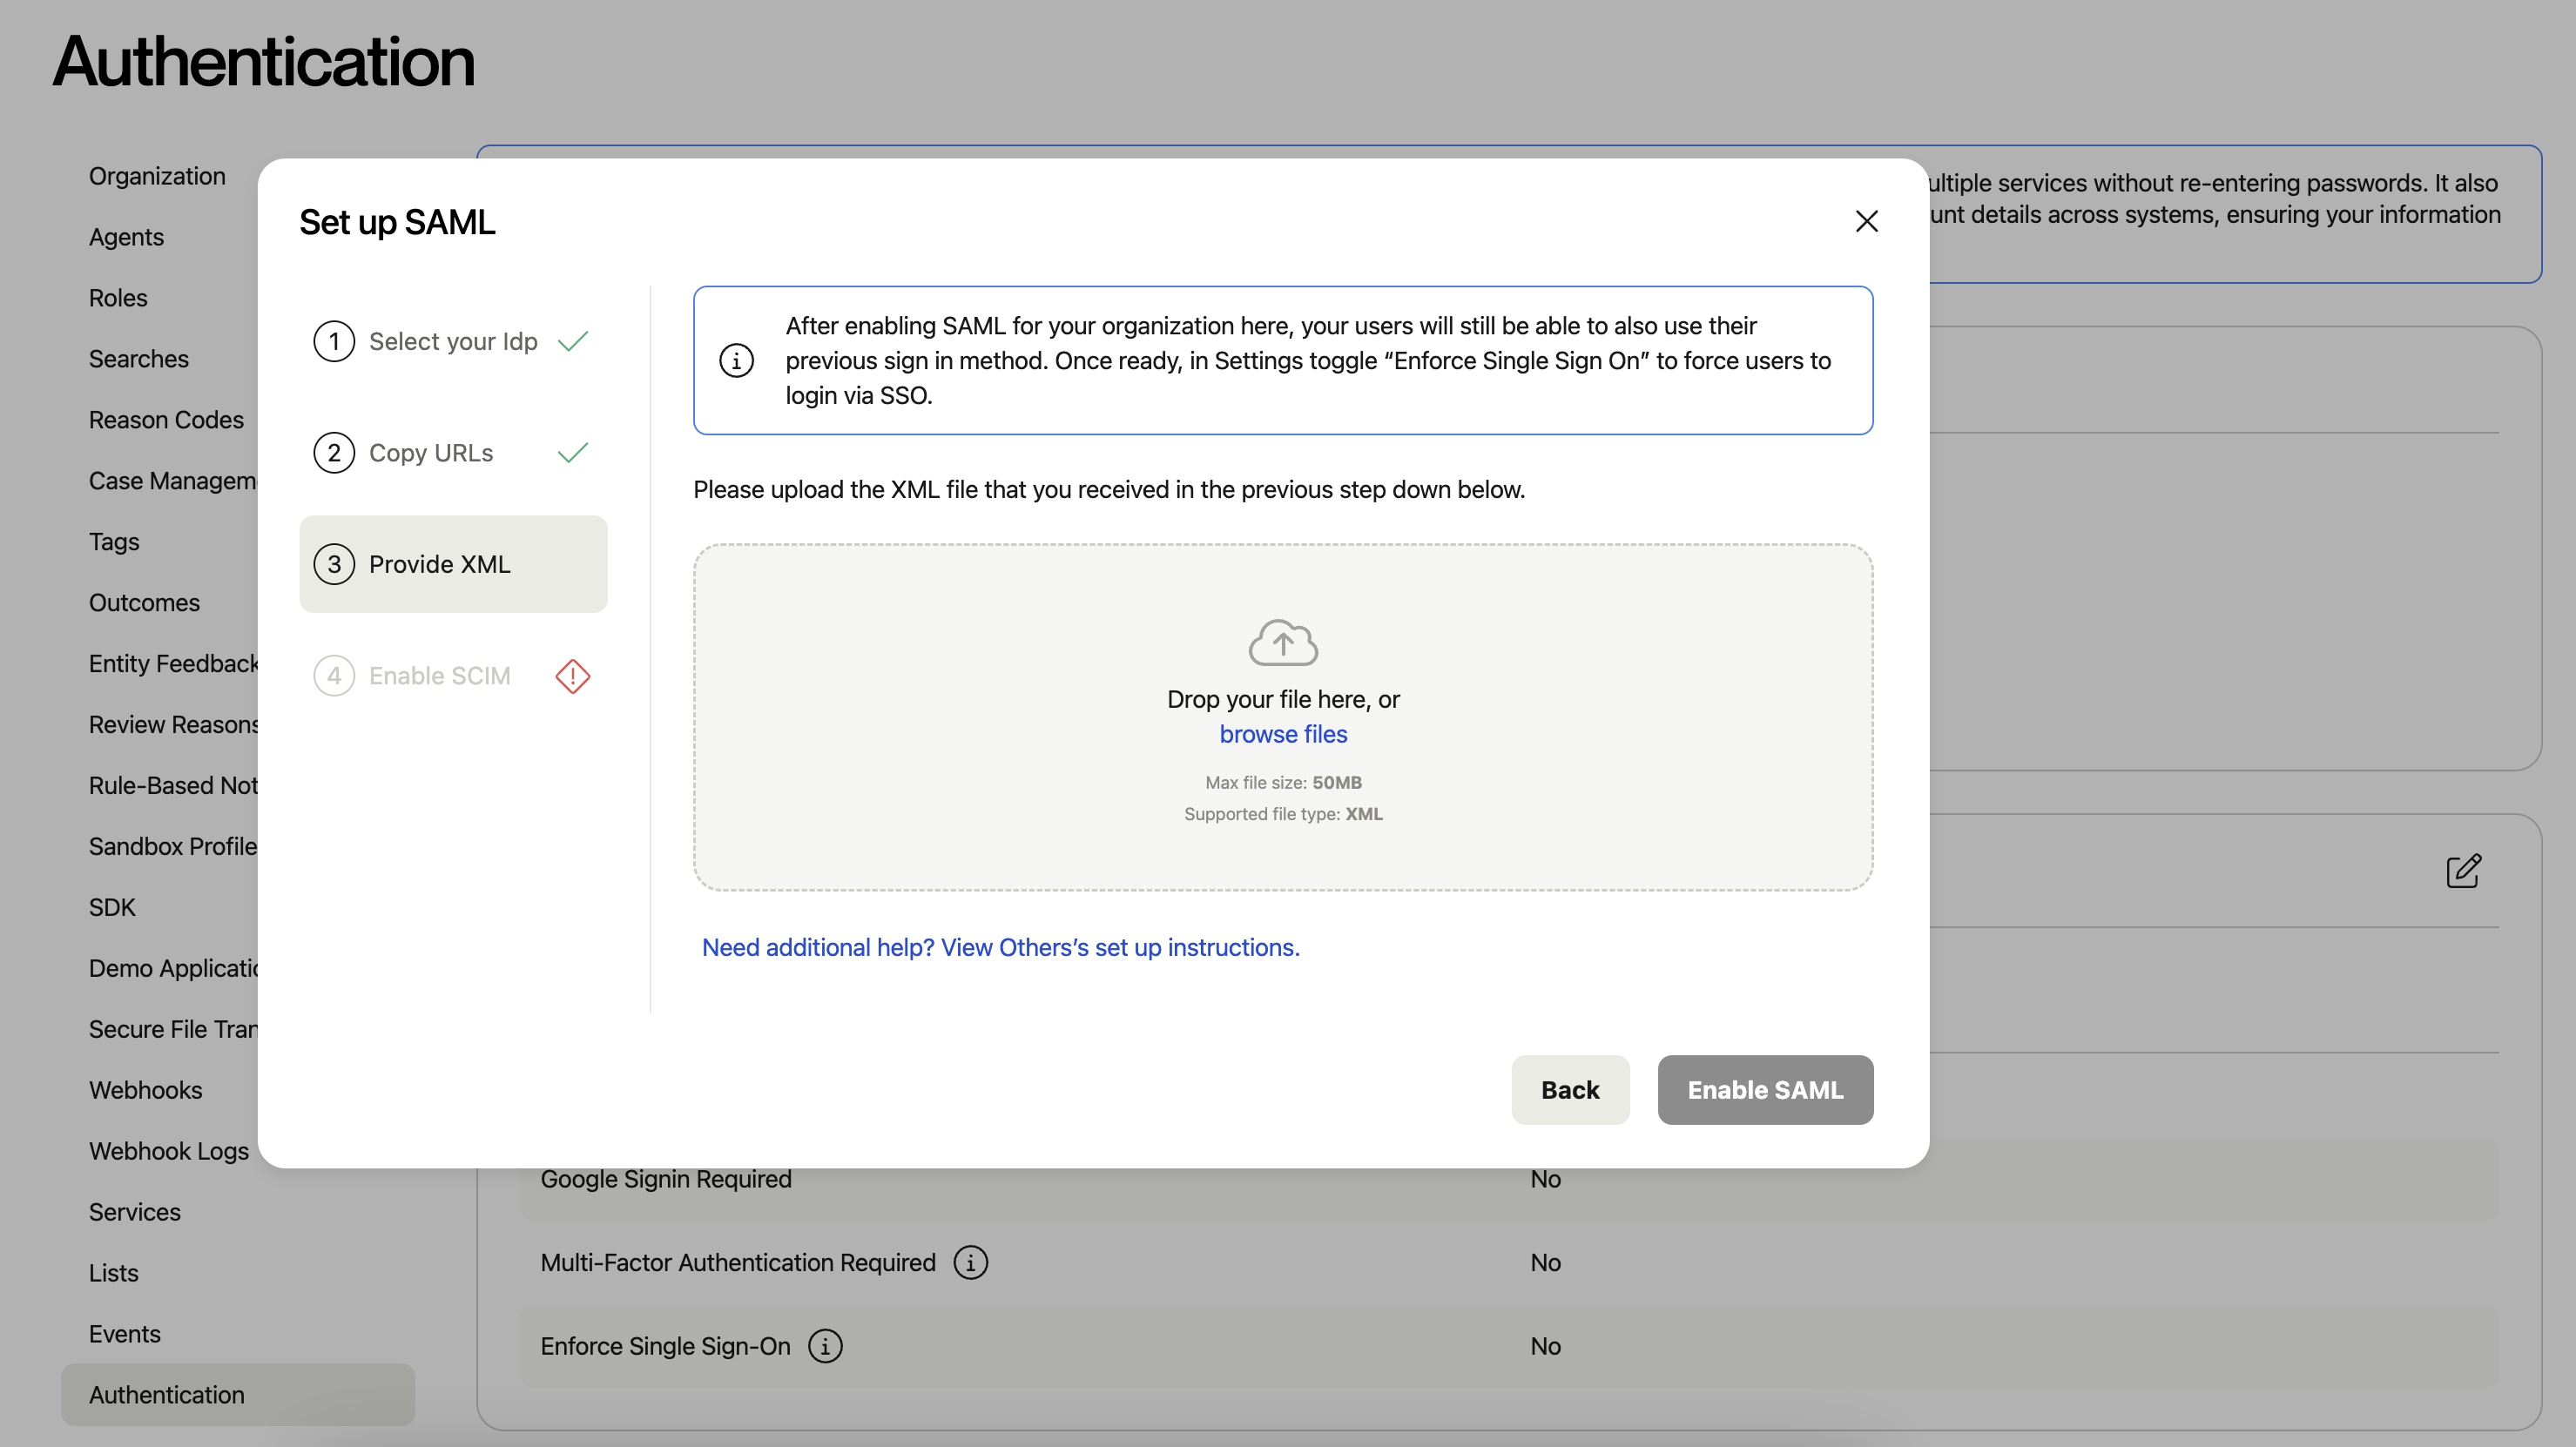
Upload the `Metadata XML` file in step 3 of the SAML setup process.
![](https://files.readme.io/45a2ccba92d27a76eaf0709533fa21e65e7f8cd52cca05bb6df8fb4d6b4565ed-image.png)

***

## 4. Test the Single Sign-On

### 4.1 Assign the User to the App

<Image title="Screenshot 2024-04-26 at 6.05.16 PM.png" alt="Assigning a user to the application in JumpCloud." align="center" src="https://files.readme.io/87aa510-12.png" />

### 4.2 Test SSO with the Assigned User

1. Log in to the JumpCloud Portal.
2. Test the Single Sign-On process.

***

## 5. Other Authentication Settings

<Image title="Screenshot 2024-04-16 at 4.18.49 PM.png" alt="Other Auth Settings in Alloy." align="center" src="https://files.readme.io/cb7bdb2-5.png" />

* **G Suite Domain**: Enter the G Suite Domain for Google SSO logins.
* **Google Sign-in Required**: Force users to log in via Google SSO.
* **Multi-Factor Authentication Required**: Require MFA if SAML is not enabled.
* **Enforce Single Sign-On**: Force all users to log in with SSO if enabled.

***

### 5.1 SAML Exceptions

If you’d like to grant users the ability to log in via credentials while **Enforce Single Sign-On** is enabled, configure this via the "SAML Exceptions" section.

<Image title="Screenshot 2024-04-16 at 4.23.19 PM.png" alt="Configuring SAML exceptions in Alloy." align="center" src="https://files.readme.io/6864d39-6.png" />