---
updatedAt: 2026-09-16T16:50:16.000Z
agentTools:
projectIndex: https://developer.alloy.com/public/llms.txt
---
# Azure
### 1. Enable SCIM
1. Open the application that is configured for SAML in the Entra Id admin dashboard. Then select **Provisioning** on the left sub-nav
2. If this is the first time Provisioning is being configured, an informational screen will be presented. Select **“Connect your application”. **if this is not the first time configuring Provisioning, select **"Connectivity".**
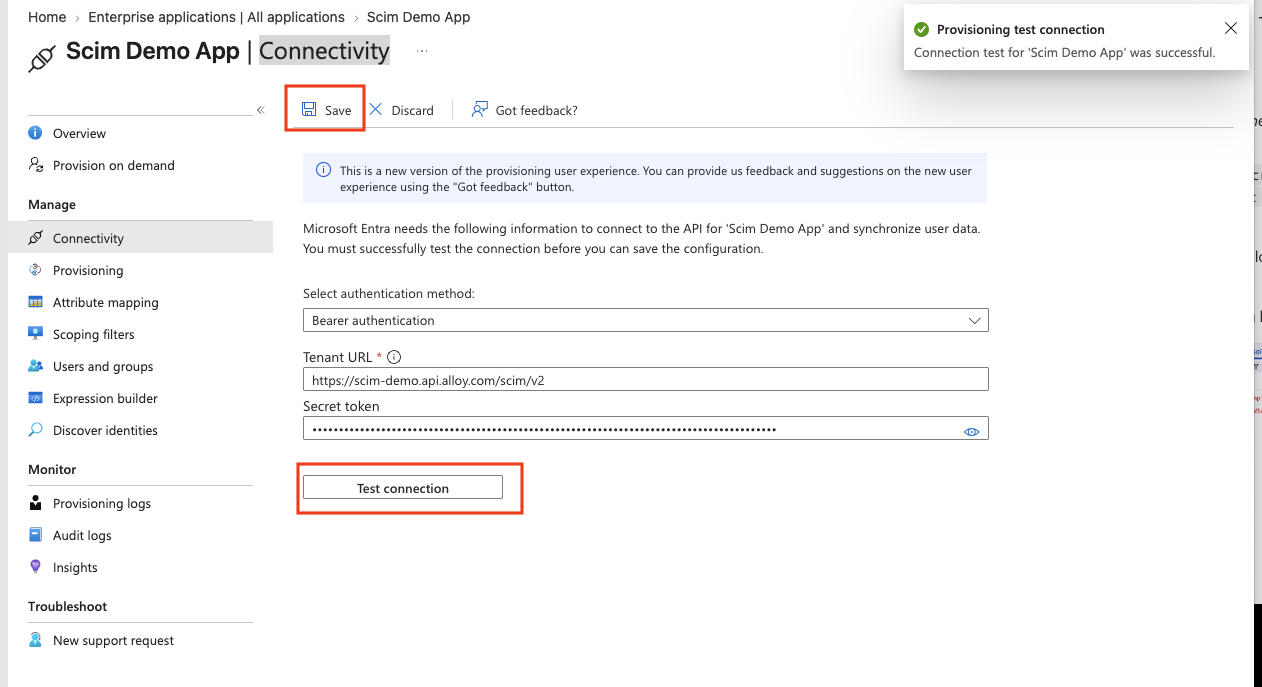
3. On the Connectivity page, enter the following values:
* **Select authentication method**: `Bearer authentication`
* **Tenant URL**: `https:///scim/v2`
* Your API domain is similar to your Alloy application domain, but uses api instead of app.
For example:
* Application domain: scim-demo.**app**.alloy.com
* API domain: scim-demo.**api**.alloy.com
* Tenant URL:
- **Secret Token**: ``
* You can create your `alloy_api_token` and `alloy_api_secret` in the Alloy dashboard under **Settings > API Keys**.
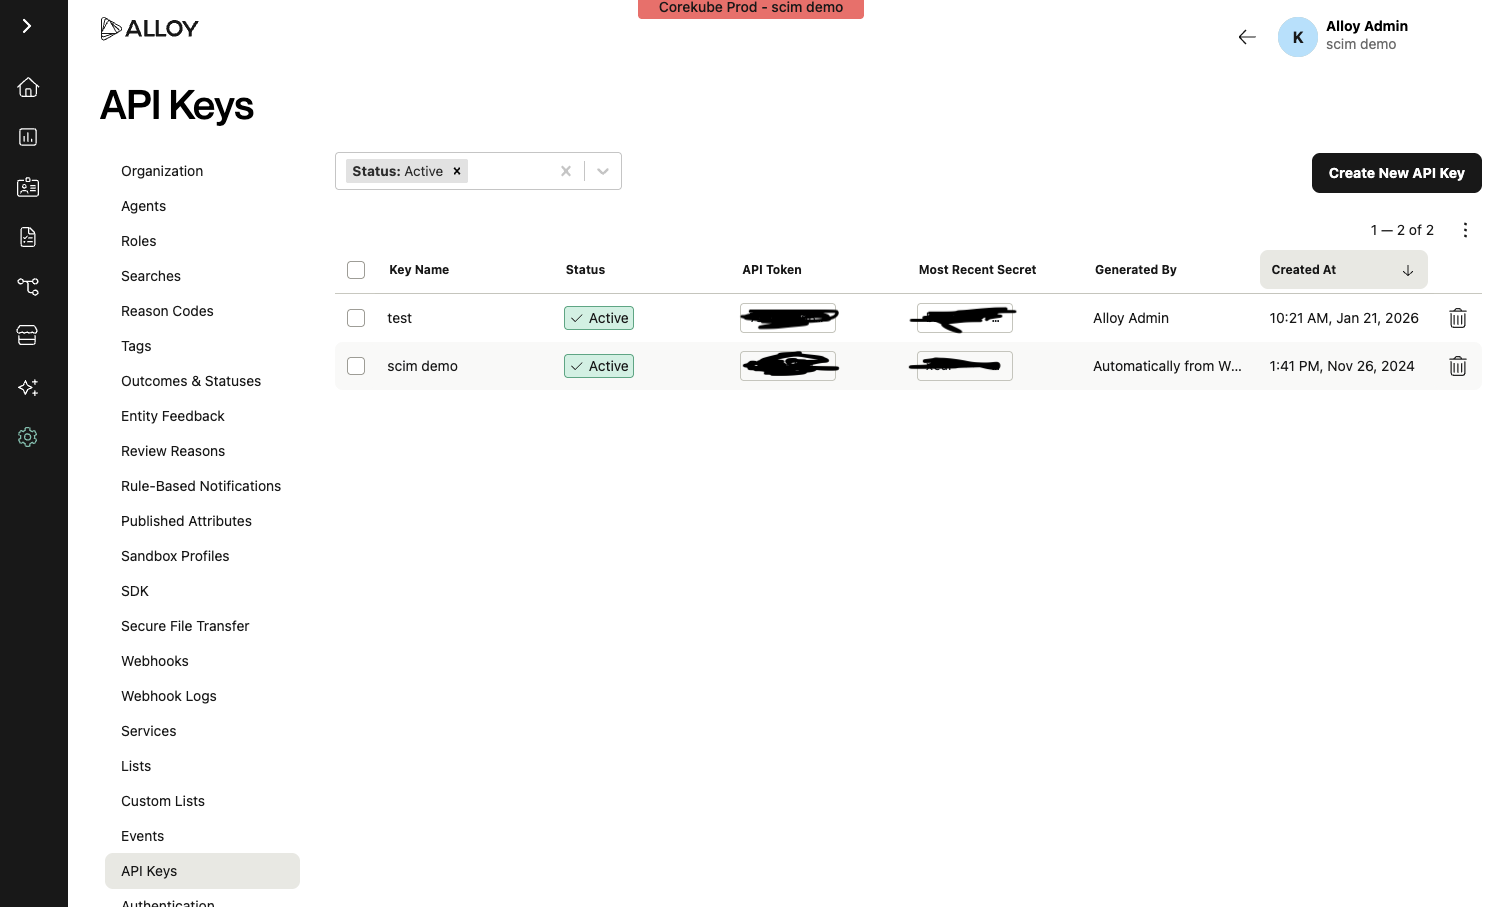
* To create the **Secret Token**, Base64-encode the API token and secret in the following format:
alloy\_api\_token:alloy\_api\_secret
For example, you can run the following command in your browser's developer console:
`btoa("alloy_api_token:alloy_api_secret")`
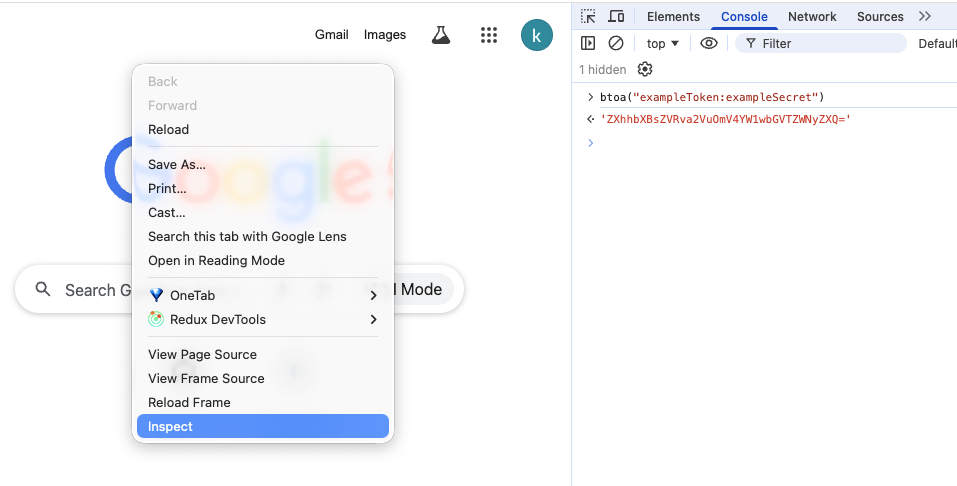
Enter only the resulting Base64-encoded value in the **Secret Token** field. Do not add a prefix such as `Bearer`.
For more information, see the [Alloy authentication guide](https://developer.alloy.com/public/docs/authentication-guide#:~:text=base64_encode\(workflow_token%3Aworkflow_secret\)-,OAuth%202.0,-To%20authorize%20once). Alloy currently supports only Bearer authentication for SCIM.
- Select Test Connection. After Microsoft Entra ID successfully connects to Alloy, select Save.
4. Once the saving process is complete, scroll down as the toggle header **Mappings** should now be visible. Select **Provisioning Microsoft Entra ID Users.**
5. Modify the Users **Attribute Mapping** to mirror the below image then select **Save**. That’s it! SCIM Provisioning is now configured. (`phoneNumbers[type eq "mobile"].value`is optional)
### 2. Assign Users to Alloy app.
1. Open the application that is configured for SAML in the Entra Id admin dashboard and select **Assign users and groups** or **select Users and Groups** on the left sub nav.
2. The application may already contain assigned users. To assign a user, select “**Add user/group”.** A modal should display. Select **“None Selected”** to begin selecting users to assign.
3. Click **“Select”** then **“Assign”** to complete the process.
4. Navigate to **“Provisioning”** on the left sub-nav.
5. The user has been assigned to the application on Entra Id. Entra Id updates Alloy with these changes on a 40 mins fixed interval basis. Due to the secret token’s short lifespan (1hr), its recommended to use the “\*\*Provision on demand “\*\*option when attempting to synchronize a small number users or groups.
6. **Provisioning on Demand**. After clicking **Provision**, any changes made to the users active status, first name, last name, or phone number will propagate to Alloy.
### 3. Assign Groups to Alloy app
1. Open the application that is configured for SAML in the Entra Id admin dashboard and select **Assign users and groups** or **select Users and Groups** on the left sub nav.
2. To assign a Group, select “**Add user/group”.** A modal should display. Select **“None Selected”** to begin selecting groups to assign.
*Please note:💡: To assign a group to an existing role, make sure the group name ****exactly matches**** the role within Alloy. Any users assigned to that group will be provisioned into the corresponding Alloy role.*
3. Click **“Select”** then **“Assign”** to complete the process.
4. Navigate to **“Provisioning”** on the left sub-nav.
5. The group has been assigned to the application on Entra Id. Entra Id updates Alloy with these changes on a 40-minute fixed interval basis. Due to the secret token’s short lifespan (1hr), it's recommended to use the “\*\*Provision on demand “\*\*option when attempting to synchronize a small number of users or groups.
6. **Provisioning on Demand**. After clicking **Provision**, any changes made to the group's name will propagate to Alloy.
### 4. Verify the User and Groups created on the Alloy app
1. Login to the Alloy app. go to the settings, nav to Agents and Groups page. verify the user and group are added to the Alloy app